
Blog
 RSS feed
Leadership · Thu Jul 02, 2026
Mythos-Class AI and the End of the Patch Window
Mythos-class models are compressing vulnerability discovery and exploitation timelines. For defenders, the practical question is no longer only how fast they patch, but whether their controls detect exploitation when the patch window disappears.
Aarush Ahuja
Leadership · Thu 18 Jun, 2026
Meet Your Tireless Red Teamer: Continuous Validation for AI-Assisted Attacks
CrowdStrike’s 2026 Global Threat Report found AI-enabled adversaries increased activity by 89%. As attackers become faster and more adaptive, FourCore ATTACK helps teams assess defenses, validate control effectiveness, and improve remediation against real exploitable gaps.
Aarush Ahuja
Leadership · Thu 11 Jun, 2026
What CERT-In’s AI Threat Blueprint Means for Adversarial Exposure Validation
CERT-In’s blueprint points toward a cybersecurity model that is continuous, threat-informed, and evidence-led. Here is what that means in practice, and how adversarial exposure validation helps organisations test whether their controls actually work against AI-assisted threats.
FourCore

Integration · Wed 27 May, 2025
Threat-informed defense with HarfangLab EDR and FourCore ATTACK
Adversary emulation is a key component of Threat-informed defense. This post details emulating Microsoft Edge browser data theft using FourCore ATTACK and validating detections with HarfangLab EDR to enhance security posture.
Swapnil
Success Story · Mon April 01, 2024
Customer Success Story: Defense Contractor in The Middle East Improves Detection and Response
How a defense contractor with more than 5000 employees improved threat visibility in just a week with FourCore ATTACK. Validating and optimizing security controls across endpoints and maximizing the effectiveness of their industry-leading EDR and SIEM.
Aarush Ahuja
Integration · Sun 17 Dec, 2023
Threat-informed defense with LimaCharlie and FourCore ATTACK
Adversary emulation is a key component of Threat-informed defense. It is about impersonation, mimicking threat actors and their TTPs. The FourCore ATTACK adversary emulation platform automates emulation of threats and integrates with LimaCharlie to validate alerts and detections for these threats in real time.
Aarush Ahuja
Article · Mon Dec 12, 2023
Rhysida Ransomware: History, TTPs and Adversary Emulation Plans
Rhysida is a new player in the Ransomware space, first appearing in May 2023, and has been targeting industries all across the globe. In recent months, Rhysida has run campaigns compromising and extorting organizations from the government, education, healthcare, IT, and manufacturing sectors. Rhysida emerged in the Ransomware Space with a high-profile attack on the Chilean army. The group currently has more than 50 victims listed on its leak site.
Swapnil

Article · Thu Oct 26, 2023
Threat Hunting: Detecting Browser Credential Stealing [T1555.003]
Adversaries can steal credentials, cookies and other private data from browsers using various techniques. We cover how you can simulate Credential Stealing From Browser s and detect it with your security tools. Sigma Rules Inside.
Parth Gol
Article · Mon Jul 17, 2023
CVE-2023-36884 MS Office Zero-Day Vulnerability Exploited For Espionage - Detection and Mitigation
Microsoft has warned of six unpatched zero-day vulnerabilities including CVE-2023-36884 being exploited by attackers for financial and espionage motives. No patches are available for CVE-2023-36884, find the mitigations and detections to prevent CVE-2023-36884.
Aarush Ahuja
Article · Tue Jun 03, 2023
Clop Ransomware: History, Timeline, And Adversary Simulation
The infamous Clop ransomware, mainly known as Cl0p, targets various industries and organizations, extorting data for a huge amount of ransom. It advances actively with new emerging campaigns. This blog walks through the Clop timeline, Mitre TTPs and their emulation.
Jones Martin
Research · Thu Feb 16, 2023
TrustedInstaller Bypass: How to Delete Windows Defender
How to obtain TrustedInstaller privileges on Windows, bypass tamper protection, and access the Defender directory using token manipulation.
Swapnil
Article · Sun Jan 29, 2023
A Malicious Note: Hackers using Microsoft OneNote Attachments to spread malware
Attackers are constantly looking for novel approaches to infect users with malware. Recently, hackers have been using OneNote attachments in phishing emails to spread malware and password stealers to their victims.
Hardik Manocha
Article · Sun Jan 08, 2023
Exploit Party: Bring Your Own Vulnerable Driver Attacks
BYOVD or Bring Your Own Vulnerable Driver is an attack where a threat actor brings a legitimately signed and vulnerable driver to perform malicious actions on the system. In a BYOVD attack, the attacker can use the vulnerabilities in the driver to execute malicious actions with kernel-level privileges!
Swapnil
Integration · Wed Jan 04, 2023
Honey, I shrunk the SOC: Measuring Threat Visibility with MITRE ATT&CK(R)
We are excited to partner with Tidal Cyber and release our repository of attack simulations on the Tidal platform to help pave the way forward for operationalizing threat-informed defense.
Aarush Ahuja
Article · Mon Oct 28, 2022
EDR: Detections, Bypassess and other Shenanigans
EDR or Endpoint Detection and Response refers to an integrated endpoint security solution which continuously monitors end-point user's devices and try to prevent anomalies like Malware, Ransomware by using automated rule based response method.
Sourav Sen
Article · Fri Sept 30, 2022
Microsoft Exchange Zero-Day Actively Exploited In Attacks: How to Mitigate
As of 30th Sept. 2022, A new zero-day is being actively exploited on Microsoft Exchange servers. MSRC has published guidance for customers to mitigate the vulnerability.
Aarush Ahuja
Article · Fri Sept 29, 2022
WhatsApp zero-day bug: What you need to know
WhatsApp silently fixed two zero-day vulnerabilities in their Android and iOS applications. These vulnerabilities let hackers take full control of the app remotely and execute arbitrary code. The two vulnerabilities are: CVE-2022-36934, an integer overflow bug on iOS and Android and CVE-2022-27492, an integer underflow bug on iOS and Android.
Aarush Ahuja
Article · Wed Aug 31, 2022
Ryuk Ransomware: History, Timeline, and Adversary Simulation
Ryuk is ransomware attributed to the hacker group WIZARD SPIDER that has targeted governments, healthcare, manufacturing, and technology organizations. This article covers the Ryuk Attack, Threat Intel on Ryuk Ransomware, Attack Vectors involved, attack flow, IOCs and detection rules.
Hardik Manocha
Article · Sat Aug 20, 2022
Detection Engineering with MITRE Top Techniques & Atomic Red Team
Detection Engineering is the process of optimizing security controls to get the most value out of them. Therefore, it is essential to prioritize your efforts according to your organization's needs and requirements. Here we cover the methodology of Detection Engineering using MITRE Top Techniques Project and Atomic Red Team.
Swapnil
Article · Sat Aug 13, 2022
ATT&CK + D3FEND = D.E.A.T.H
Threats targeting cyberspace are becoming more prominent and intelligent day by day. This inherently leads to a dire demand for continuous security validation and testing. By combining the power of MITRE ATT&CK and MITRE Defend, security practitioners can effectively address threats responsibly.
Hardik Manocha
Article · Fri Aug 5, 2022
New Era of Phishing Payloads
Post the Office macros deprecation, a new malware delivery method is on the rise. Container file formats like ISOs/RARs/ZIPs and LNKs/DLLs can bypass Mark-of-the-Web, Microsoft’s prime defence.
Ratan Gupta
Article · Wed Jul 27, 2022
Manipulating Windows Tokens with Go
Windows Tokens are used for authentication and assigning privileges to windows programs. Understanding token manipulation is essential to detect malicious behaviours. Security professionals can use the wintoken library for token manipulation.
Swapnil
Article · Sun Jul 24, 2022
10 Open-Source Adversary Emulation Tools (2026) | FourCore
Compare open-source adversary emulation tools including MITRE Caldera, Atomic Red Team, Stratus Red Team, and Firedrill by ATT&CK coverage and use case.
Hardik Manocha
Article · Sat July 16, 2022
Genesis - The Birth of a Windows Process (Part 2)
What happens when you run an executable on your Windows machine? In this second and final part of the series, we will go through the exact flow CreateProcess carries out to launch a process on Windows.
Hardik Manocha
Article · Wed July 13, 2022
Genesis - The Birth of a Windows Process (Part 1)
What happens when you run an executable on your Windows machine? This blog provides a brief overview and the flow for creating a Windows Process, the APIs and structures involved, and the Process Internals.
Hardik Manocha
Article · Mon Jul 5, 2022
Raspberry Robin Worm infecting hundreds of Windows networks - Detection Sigma Rules
First spotted by the Red Canary intelligence team in Sept 2021, Raspberry Robin spreads via USB and Microsoft has discovered it to compromise hundreds of Windows networks already! Use these sigma rules to detect and prevent Raspberry Robin worm.
Aarush Ahuja
Article · Mon July 04, 2022
Jenkins discloses zero-day vulnerabilities affecting dozens of plugins
If you are a user of Jenkins, go patch! Jenkins security team announced various bugs affecting a variety of their plugins. While patches for a few plugins have been published, several are still waiting to be patched.
Hardik Manocha
Article · Tue June 21, 2022
A deep dive into Sigma rules and how to write your own threat detection rules
Sigma Rules - a generic open-source signature format for SIEM Systems. What Snort is to network traffic, and YARA to files, Sigma is to logs. Released in 2017, Sigma rules are used as a common language to build detection rules for different SIEM systems.
Hardik Manocha
Article · Tue June 14, 2022
What Is a Purple Team? Red vs Blue vs Purple Teaming
Learn how red, blue, and purple teams work together to test attack techniques, share evidence, and improve detection and response outcomes.
Hardik Manocha
Success Story · Tue Jun 07, 2022
Customer Success Story: Financial Services Firm improved threat visibility in two weeks
How a financial services firm with more than 500 employees improved threat visibility in just two weeks with FourCore ATTACK. Validating and optimizing security controls across endpoints and maximizing the effectiveness of their industry-leading EDR and SIEM.
Aarush Ahuja
Article · Mon Jun 06, 2022
Using Windows Event Log IDs for Threat Hunting
Windows logs every action with a unique event ID. Security analysts can utilize these logs for threat hunting and enrich detections to identify attackers efficiently. Let's take a look at the different tools and Event IDs you can use for threat hunting
Swapnil
Article · Mon May 30, 2022
New zero-day code execution vulnerability in MS Office - Follina
Independent security research team nao_sec reported a file submitted from Belarus exploiting the ms-msdt protocol and template injection to achieve zero-click code execution in MS Word. And this is not a good one!
Aarush Ahuja
Article · Mon May 16, 2022
F5 BIG-IP critical vulnerability exploited by attackers to gain unauthenticated RCE
If you are a user of F5 BIG-IP, go patch! CVE-2022-1388 is a vulnerability in F5 BIG-IP that allows an unauthenticated attacker to run arbitrary commands, modify files, or disable services on unpatched systems.
Aarush Ahuja
Article · Thu May 05, 2022
The curious case of mavinject.exe
Mavinject, described as Microsoft Application Visualisation Injector, is a signed Microsoft executable that can be abused to perform arbitrary code injections inside any running process.
Hardik Manocha
Article · Fri April 29, 2022
Privilege escalation vulnerabilities discovered in Linux known as Nimbuspwn
Microsoft has disclosed a group of vulnerabilities in Linux known as Nimbuspwn that allows attackers to gain root privileges on a vulnerable system. Find out if you are vulnerable.
Aarush Ahuja
Article · Tue Apr 26, 2022
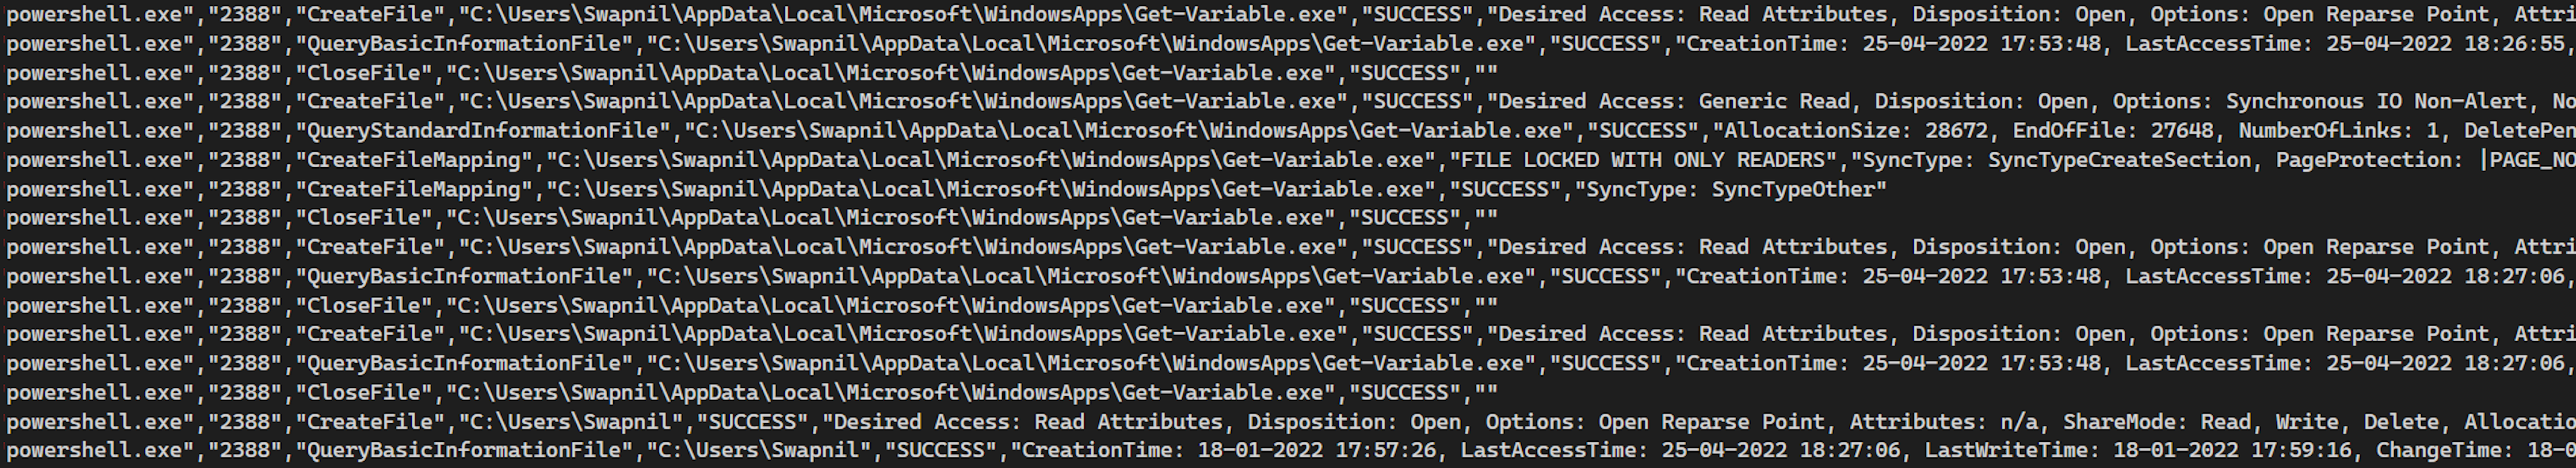
Colibri Loader's unique Persistence Technique using Get-Variable cmdlet
Colibri Loader uses a novel method of Persistence which makes use of Get-Variable cmdlet to run its executable every time powershell is launched. Here we cover the method, why it works, and how to detect such TTPs.
Swapnil
Article · Mon Apr 18, 2022
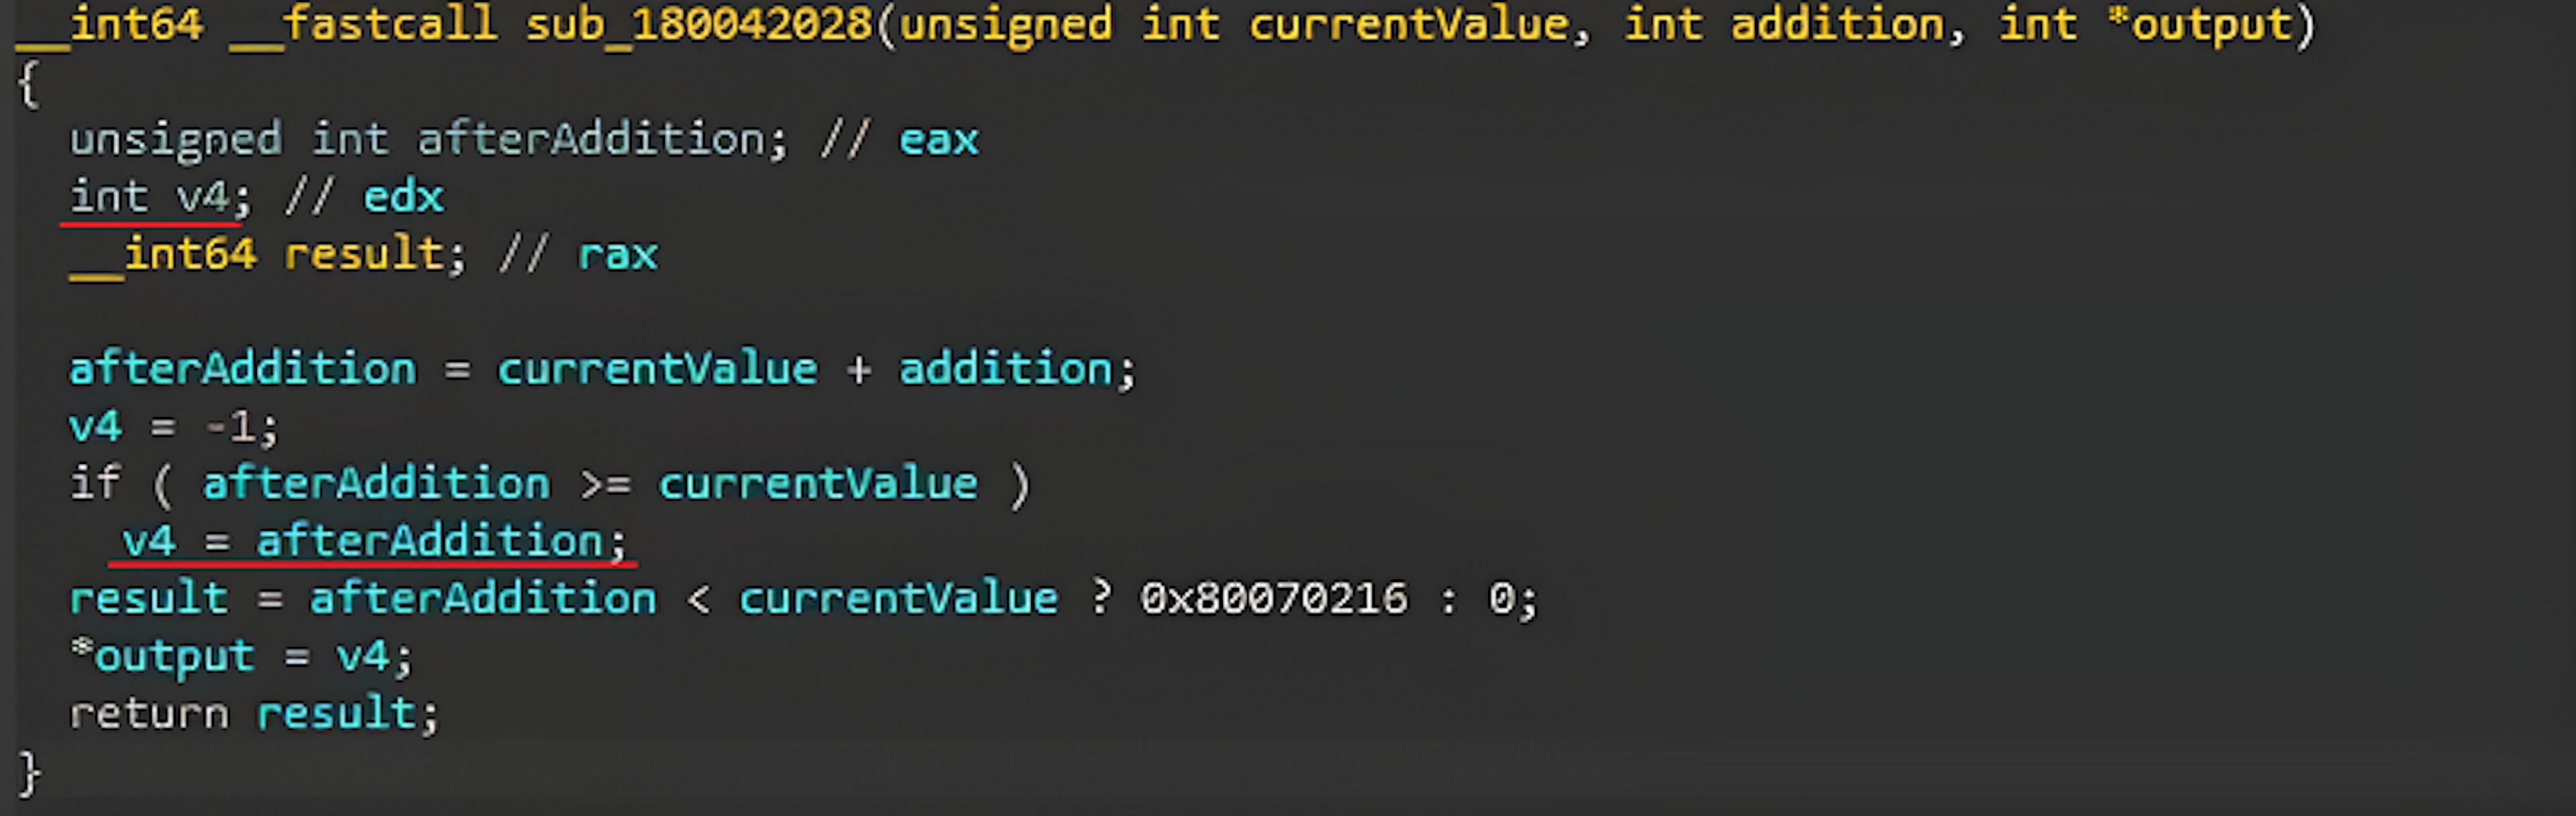
Critical Zero-Click Zero-Day Vulnerability in Windows RPC (CVE-2022-26809)
CVE-2022-26809 is a very high impact vulnerability impacting more than 700,000 Windows machines exposed to the internet. Here we cover what the vulnerabilty is, if you are vulnerable to it and how you can mitigate the vulnerability.
Aarush Ahuja
Article · Sun Jan 23, 2022
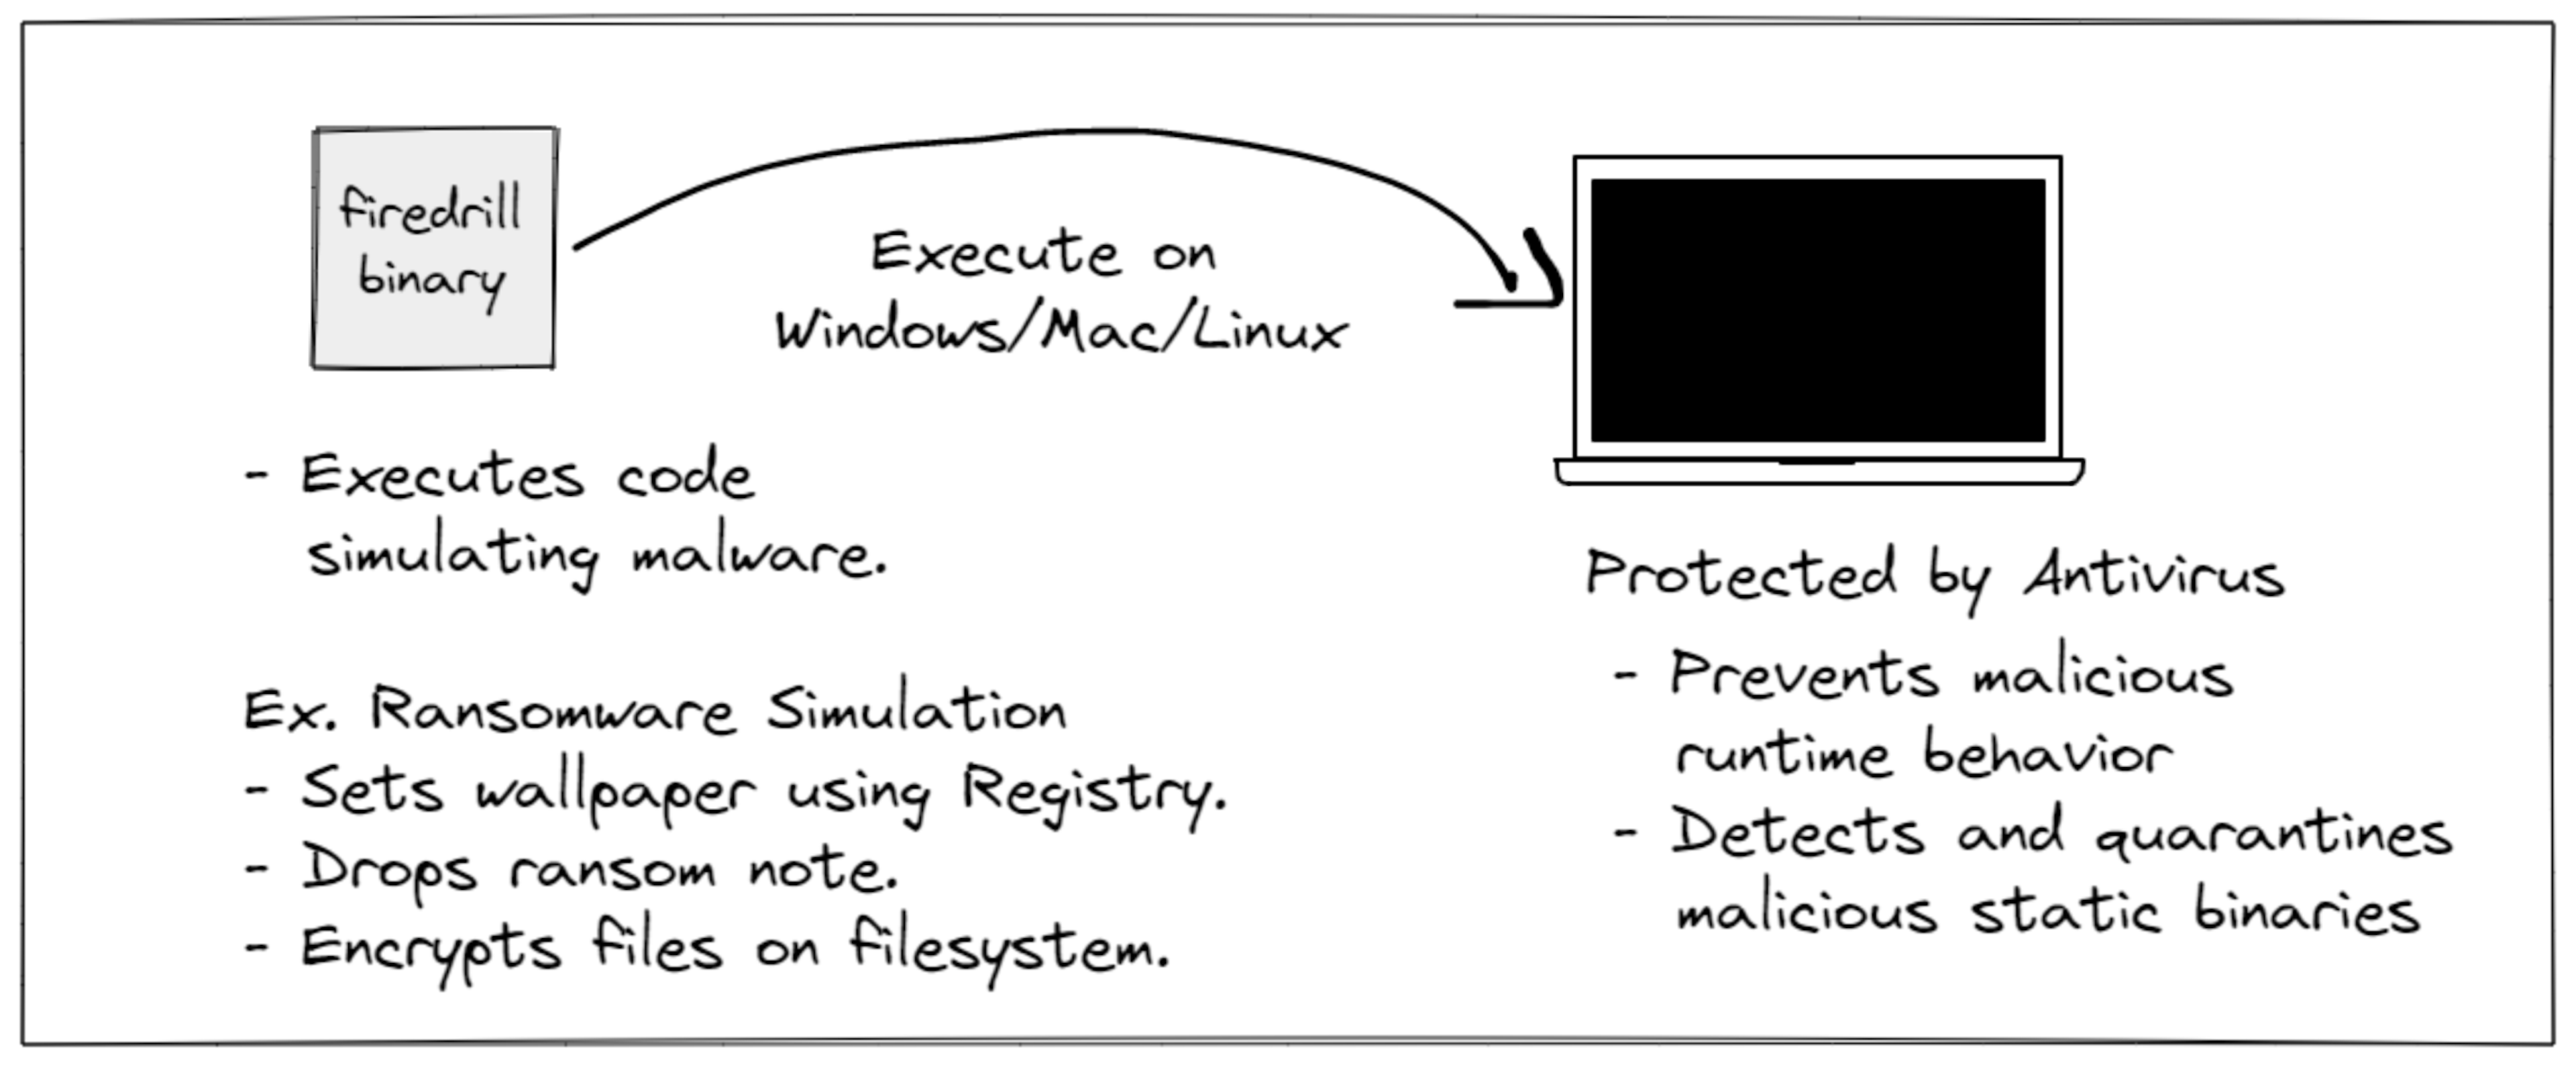
firedrill: an open source malware simulation harness
We have open-sourced firedrill, a malware simulation harness. Simulate attacker TTPs and validate your security controls. Download it now from GitHub.
Aarush Ahuja
Article · Fri Jan 14, 2022
This cyber attack can cost you $4mn.
The pandemic has accelerated the transformation of a hybrid workplace, and the expansion of the attack surface is inevitable. Although teams coordinate and engage remotely, "socially engineered" phishing attacks have become an unwanted risk and a nuisance for defenders. Phishing attacks have always been prevalent in the cybersecurity threat landscape, giving attackers a foothold into your infrastructure and wreaking havoc on organizations, with attacks and adversaries becoming more sophisticated, dynamic and persistent than ever. According to IBM, Phishing Attacks can cost organizations over $4mn in the event of a breach and is the second-most frequent reason for breaches!
Hardik Manocha
Article · Sun Oct 10, 2021
Red Team Adventure: Digging into Windows Endpoints for EDRs and profit
EDRHunt is an open-source security tool to fingerprint security solutions (such as EDRs and AVs) installed on Windows. Download the binary from GitHub.
Hardik Manocha