
New techniques as threats emerge
FourCore research adds safe versions of new attacks as threats emerge. Your coverage grows with the threats you track.
FourCore ATTACK emulates techniques on your machines and records what each control did. Your ATT&CK coverage comes from those results, technique by technique.
“How well do we cover Credential Access?”
3 gaps.
14 techniques emulated on 10 machines. 9 prevented, 2 detected, and 3 missed with no alert.
A mapping says a tool should detect a technique. An emulation shows whether it did, on your machines, with your configuration.
Emulate
The library holds 1,500+ attack procedures across 330+ MITRE ATT&CK techniques. You choose a threat, a campaign or a technique, and FourCore Analyst builds the safe chains.
Explore FourCore ATTACKTechniques selected
Four techniques from three tactics, ready to run on 10 machines.
From 1,500+ procedures across 330+ techniques
Measure
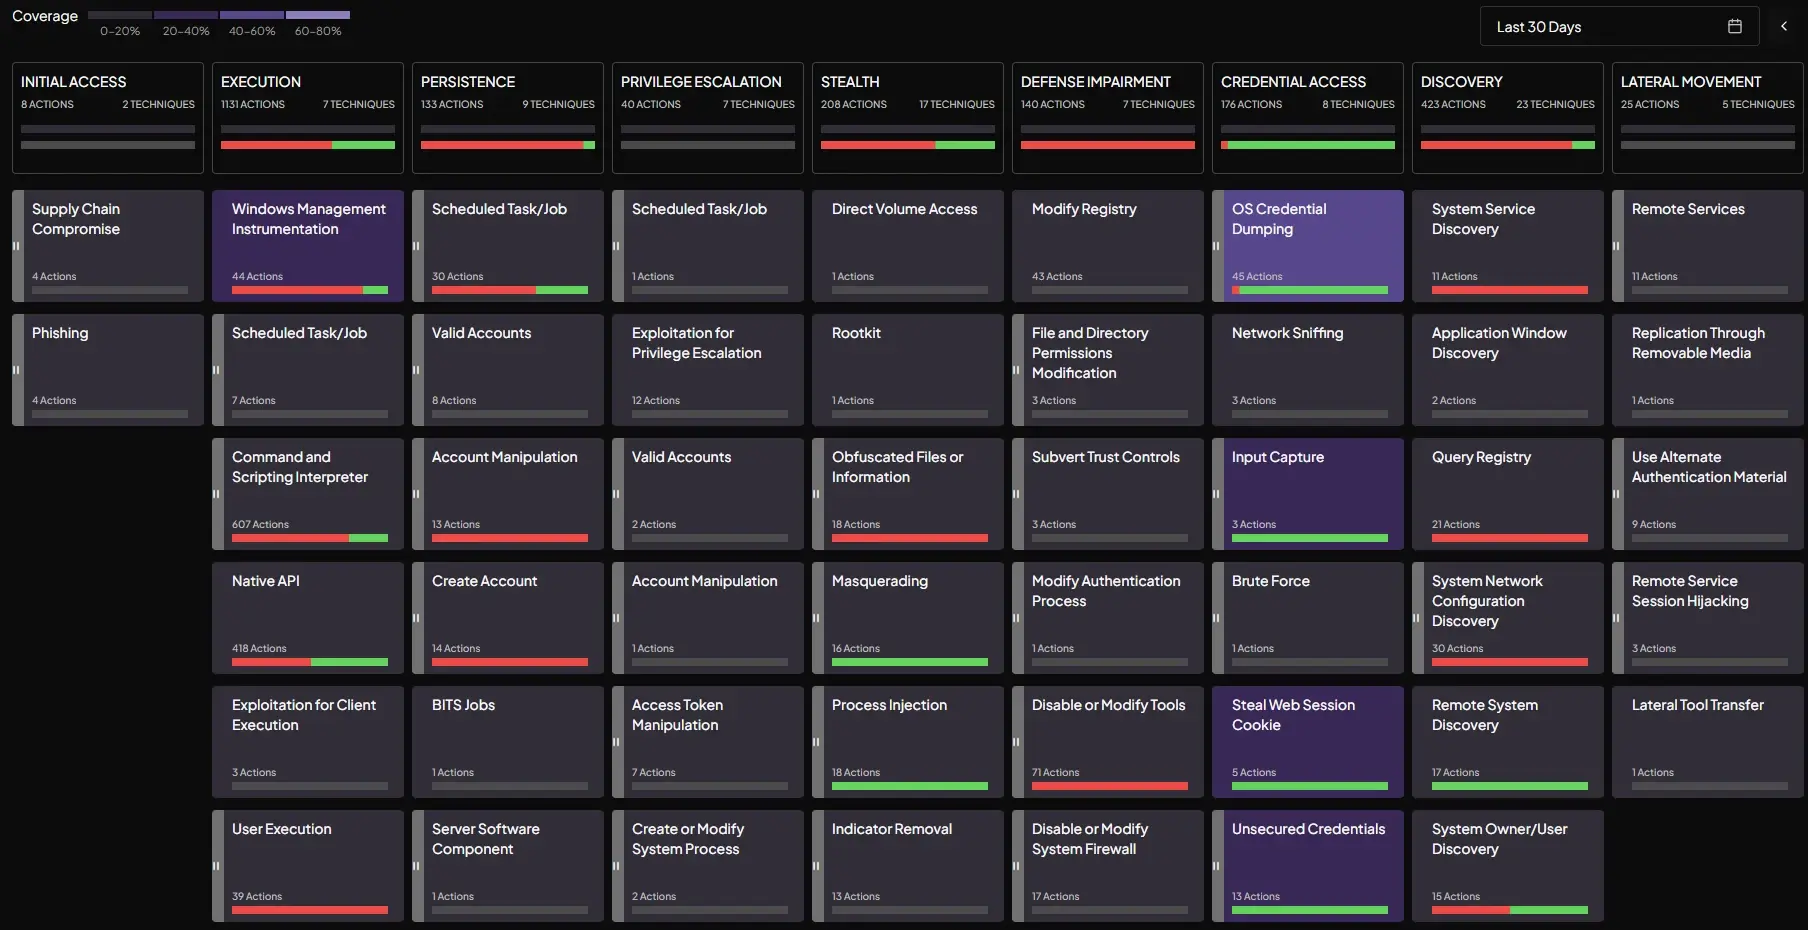
FourCore ATTACK records whether each control prevented, detected or missed each technique. Results roll up by tactic, so you see where the gaps cluster.
Coverage by tactic
Improve
FourCore Analyst writes the mitigation and the detection for each missed technique. The same emulation runs again, and your coverage updates from the new result.
T1053.005 · Scheduled task
Each emulated technique, grouped by tactic, with the result for each control.
Controls drift with each change. Re-running the same techniques shows the drift in your results before an attacker finds it.
FourCore research adds safe versions of new attacks as threats emerge. Your coverage grows with the threats you track.
Results map to MITRE ATT&CK, so detection engineers and leadership read the same coverage.
FourCore HUNT findings also map to MITRE ATT&CK. Run both, and you know what gets through and what is already inside.
Explore FourCore HUNTSee how each miss becomes a detection your SOC can rely on.
SOC validationA mapping lists what a tool should cover. FourCore records what each control did when the technique ran on your machines.
1,500+ attack procedures across 330+ MITRE ATT&CK techniques, with safe versions of new attacks added as threats emerge.
Both. Each technique records whether a control prevented it, detected it or missed it, and each miss shows its cause.
Endpoint and identity controls, SIEM detections, network and web controls, email gateways and DLP, depending on the techniques you run.
We pick the tactics that matter to you, emulate them on your machines and review the coverage with you.