FourCore ATTACK · Adversarial exposure validation: Know what your defenses stop. Fix what they miss.

Safe versions of real attacks run against your controls, and FourCore Analyst turns every gap into a tested fix.

FourCore Analystjust now

“Would the Potassium botnet's PHP2Shell exploit get past our WAF?”

Stopped.

Safe replay of the exploit against 4 web apps. The WAF blocked it on all 4 and Splunk raised an alert.

  • WAF4 blocked
  • Splunkalert raised

Your attacker's playbook, run safely every week.

Emulate the threats that target you, see which control stopped each step, and close every gap with a fix you can prove.

Dynamic adversary emulation

Every new threat, rebuilt as a safe attack

Hand FourCore Analyst a threat report, or let it pick up new research as it lands. The behaviors, malware and indicators are mapped to MITRE ATT&CK and assembled into a safe chain that runs the way the real attack does.

LiteLLM supply chain compromise

A poisoned package adds a Python startup hook that steals cloud keys. A safe chain is ready.

From the report: 5 behaviors · 9 indicators

  1. Package installs a startup hookEndpoint
  2. Hook runs on every Python startEndpoint
  3. Cloud credential files readEndpoint
  4. Keys sent to the attacker domainNetwork

Validate

Blocked, detected or missed, for every step

The chain runs on your machines and through your network and web controls. Each step is matched to the alerts in your EDR and SIEM, and every miss comes with its cause, so the fix goes to the right owner.

How Breach and Attack Simulation works

ValleyRAT sideloading chain

  • Signed profiler loads a rogue DLL

    EDR

    Detected
  • Scheduled task for persistence

    EDR

    Missed

    Sensor saw it, rule missing

  • Browser credentials read

    EDR

    Blocked
  • Command and control over HTTPS

    Web proxy

    Blocked

Improve

A fix for every gap, proven by a retest

Each gap gets the change that stops it and a detection rule written for your own tool. Your team applies it, and the same chain runs again to show the gap is closed.

Fix plan

Stop it
Allow scheduled tasks from admin tooling only
Detect it
Persistence rule, tested on 30 days of your data
Validate it
Same chain, same 6 machines
Retest Detected on 6 of 6

From a new threat to a proven fix.

Specialist FourCore Analyst agents hand the work along, and your team steps in for the two decisions that need a person.

Intel

Sim

Fix

You

  1. Research

    Pulls each behavior out of the report.

    6 behaviors
  2. Build

    Assembles the attack from library actions.

    6-step chain
  3. Approve

    Your team approves the run.

    Run approved
  4. Explain

    Reads every step and finds why each miss happened.

    2 gaps explained
  5. Write the fix

    A change to stop it and a rule to detect it.

    1 change, 1 rule
  6. Apply

    Your team applies the change.

    Change applied
  7. Retest

    The same attack runs again to prove the fix.

    5 of 5 detected

Every control in the path of an attack.

One light agent on Windows, Linux and macOS. Email and WAF assessments need no agent.

attack procedures
1,500+attack procedures
MITRE ATT&CK techniques
330+MITRE ATT&CK techniques
test cases
10,000+test cases
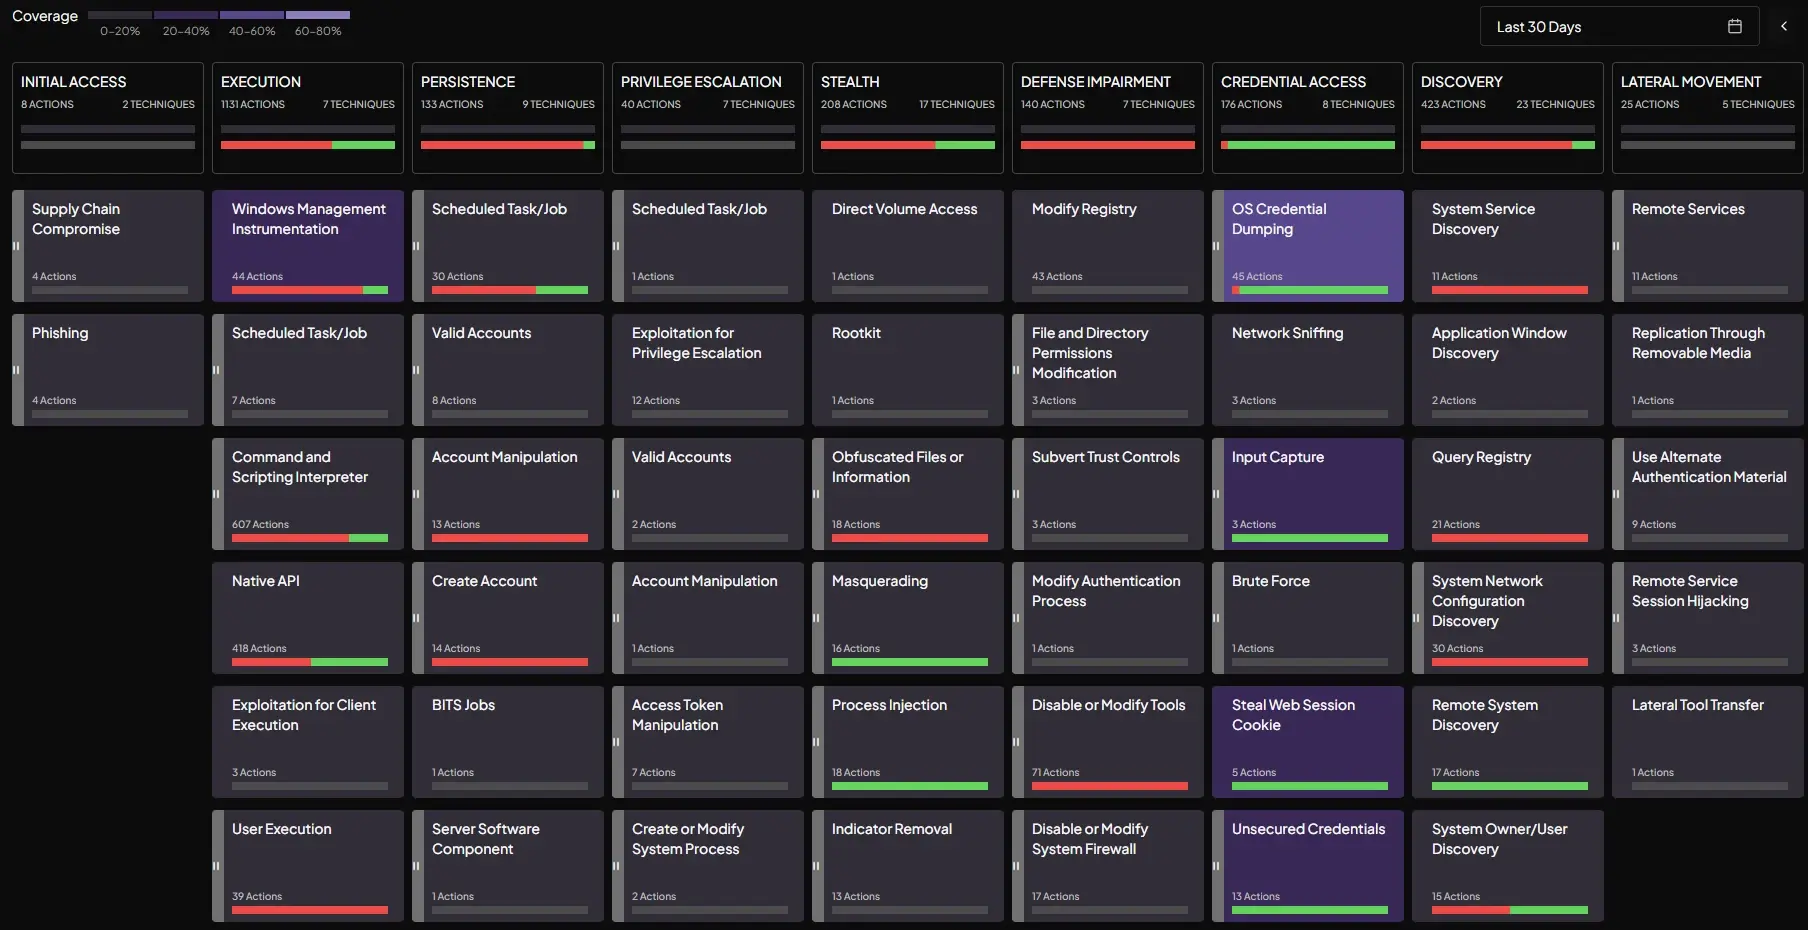
FourCore ATTACK MITRE ATT&CK coverage view, with tested techniques grouped by tactic and results for each
Coverage in FourCore ATTACK: every technique tested, grouped by tactic, with what was stopped and what got through.
  • Endpoint and identity

    EDR, antivirus, ransomware paths and Active Directory lateral movement.

  • Detection stack

    SIEM logs, correlations and alerts, with Sigma rules for your vendors.

  • Network and application

    Web proxy, IDPS, WAF and email gateway assessments.

  • Data protection

    DLP, tested with controlled exfiltration of test data.

Validation that keeps up with attackers.

Controls drift with every change. ATTACK keeps testing, so the drift shows up in your results before an attacker finds it.

Proof down to the command line

Every step keeps its output, event logs and indicators, mapped to MITRE ATT&CK and matched against what your EDR and SIEM saw. The same record rolls up into coverage by control and by machine, so the report your leadership reads is built from evidence.

T1053.005Scheduled task for persistencefin-lt-04
Output
schtasks /create /tn "OneDrive Sync" /sc onlogon
  /tr C:\Users\Public\sync.exe
SUCCESS: The scheduled task was created.
Event log
  • 4698 · A scheduled task was created
  • 4688 · schtasks.exe started by sync.exe
Indicators

sync.exe · 3f9a…c21e · task “OneDrive Sync”

Matched against your tools

  • CrowdStrikeTelemetry, no alert
  • Microsoft SentinelNo alert

Missed · rule missing

The sensor recorded the task. No rule fired on it.

This week's threats, ready to test

FourCore research adds safe versions of new attacks as threats emerge, alongside the 1,500+ procedures already in the library.

  • LoaderValleyRAT DLL sideloadingReady
  • Supply chainLiteLLM startup-hook persistenceReady
  • ExploitPHP2Shell remote code executionReady

Results read before your team logs in

FourCore Analyst AI agents run the scheduled tests overnight, read every step on every machine, and sort each miss into a missing rule or a missing sensor.

What changed overnight?

FourCore Analyst

41 steps ran on 12 machines. 3 were missed: two need a CrowdStrike rule, and one laptop has no sensor. The fixes are drafted.

Safe for production.

Controlled and non-destructive
Real techniques with no live malware, run within rules of engagement you agree up front.
Automatic cleanup
Every run removes what it created, so machines are left as they were found.
Runs within the approvals you set
New tests, scopes and schedules wait for approval, and FourCore Analyst works inside those limits.
Your team applies every change
Fixes and detection rules come written for you, and people decide what goes into production.

Questions

Is it safe to run in production?

Yes. Simulations are controlled and non-destructive, run within rules of engagement you agree, and clean up after themselves. No live malware spreads.

What does FourCore ATTACK test?

Endpoint and identity controls such as EDR, antivirus and Active Directory, your detection stack in the SIEM, network and application controls such as the email gateway, web proxy, IDPS and WAF, and data protection with DLP.

How is it deployed?

As SaaS with data residency in India, the UAE, Saudi Arabia or the US. A light agent runs on Windows, Linux and macOS, and email and WAF assessments are agentless. Single sign-on, role-based access and audit logs are included.

How is it different from a penetration test?

A penetration test is a point-in-time exercise. ATTACK runs the same attacks continuously and retests every fix, so you see when a control drifts after a change.

What does FourCore Analyst do in ATTACK?

It turns threat reports into tests, reads every result against your EDR and SIEM alerts, and writes the fix and detection rule for each gap. Your team approves the runs and applies every change.

How does a proof of value work?

We agree the assets, controls and threats that matter and what success means, run safe attacks on your machines, and review the results and fix plan together.

Know what your defenses stop, every week.

We agree the scope and what success means, run safe attacks on your machines, and review the results and fix plan together.